Skip to Content
A landscape photo showing a wooden gavel, a blue compliance binder, and a paper labeled regulations on a desk, with a digital shield and padlock icon overlay symbolizing cybersecurity and regulatory protection.

Compliance

Linked MSP helps organizations navigate complex regulatory requirements like CMMC, NIST, HIPAA, and PCI. We partner with your Qualified Security Assessor to ensure you’re prepared for audits, while continuously monitoring both perimeter and internal systems to safeguard personal data and payment information from evolving cyber threats

CMMC

The Cybersecurity Maturity Model Certification (CMMC) ensures that contractors working with the Department of Defense meet strict cybersecurity standards. As a Registered Practitioner Organization, Linked MSP helps your organization prepare for CMMC assessments, manage and maintain requirements, and improve your security posture.

CyberAB RPO Badge

  • Assess current cybersecurity practices
  • Implement required security controls
  • Prepare documentation for audits
  • Provide ongoing compliance support

Learn More at CMMC

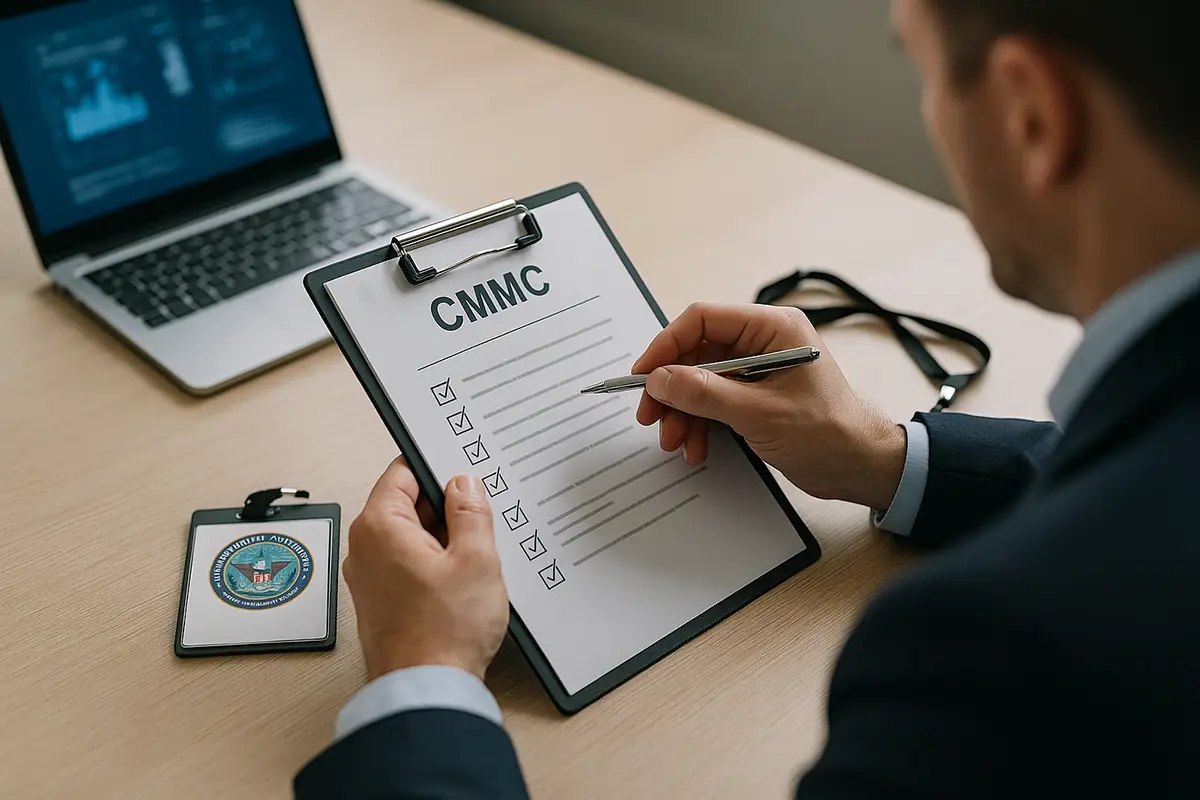
Professional reviewing a CMMC compliance checklist on a clipboard, with a Department of Defense badge and laptop on a wooden desk

NIST

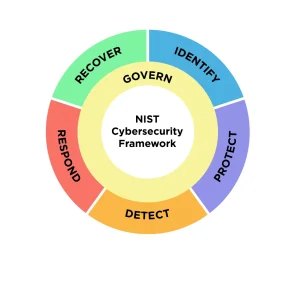
The National Institute of Standards and Technology (NIST) Cybersecurity Framework provides a flexible approach to managing cybersecurity risk. Linked MSP helps you align your organization to NIST standards, from governance to recovery.

NIST Cybersecurity Framework circle showing Govern, Identify, Protect, Detect, Respond, and Recover segments

  • Identify assets and risks
  • Develop protection strategies
  • Implement detection and response measures
  • Enhance recovery capabilities

Learn More at NIST

Close-up of the NIST acronym on a dark perforated server rack, with softly blurred server lights in the background

HIPAA

The Health Insurance Portability and Accountability Act (HIPAA) protects sensitive health information. Linked MSP, a HIPAA compliant organization, works with healthcare providers and their partners to secure electronic health records and maintain HIPAA compliance.

  • Conduct HIPAA risk assessments
  • Implement administrative, physical, and technical safeguards
  • Train staff on HIPAA requirements
  • Support incident response and breach notification

Learn More at HHS

Embossed HIPAA seal on a blue document cover, resting on a wooden surface with a shallow depth of field.

PCI

The Payment Card Industry Data Security Standard (PCI DSS) secures credit card transactions and protects cardholder data. Linked MSP, a Qualified Integrator and Reseller, helps businesses achieve PCI compliance by securing networks and meeting all required standards.

PCI Qualified Integrator and Reseller (QIR)

  • Assess PCI compliance gaps
  • Secure networks and payment systems
  • Implement encryption and access controls
  • Support compliance reporting and audits

Learn More at PCI Security Standards Council

Person inserting a credit card into a POS terminal, with a glowing digital shield and padlock icon overlay symbolizing payment security.
Close-up of a person’s finger about to press a 'Get Started' key on a modern keyboard, symbolizing initiating IT services or onboarding with Linked MSP.

Ready to Get Started?

Take the next step toward reliable, proactive IT solutions. Let us know you're interested in Compliance and we'll tailor your support from the start.

Get Started with
Compliance